Information Security and Personal Information Protection
Basic Approach
As digital technology becomes more sophisticated and widely used, the protection of information assets has become an important management foundation that supports business competitiveness and business continuity. The occurrence of an information security incident not only poses the risk of undermining our competitiveness and interrupting business, but may also lead to fines for legal violations and damage to our social credibility. Aware of these risks, the Teijin Group considers information security to be a priority risk and is working to maintain and improve information security throughout the Group in accordance with the basic policy set out in the Teijin Group Regulations for Information. To address information security risks, such as the leakage or falsification of confidential information, we work to identify physical, technical, and human threats and vulnerabilities, and continuously promote efforts to improve the security level of the entire Group. The Teijin Group has also established the Teijin Group Regulations for Personal Information Protection as its basic policy on the protection of personal information, and we are responding appropriately to personal information protection laws, for which legislation is advancing globally.
Teijin Group Regulations for Information
The Teijin Group has established the Teijin Group Regulations for Information to define the basic policies for information management, information security, and the enhancement of information effectiveness, while promoting the advanced use of information, including the utilization of digital technologies. Through strengthened governance and the promotion of strategic initiatives that support these efforts, we aim to maximize the value of our information assets and enhance the competitiveness and corporate value of the Teijin Group as a whole.
Basic Policies
- 1.The Teijin Group enhances its corporate value by considering the Information Assets to be important management resources and utilizing them actively.
- 2.The Teijin Group endeavors to maintain and improve the Information Security and the Effectiveness in handling the Information Assets.
- 3.The Teijin Group improves the competitiveness of its businesses and enhances its corporate value by promoting the advanced use of Information, including the utilization of digital technologies, and by strengthening Governance and implementing strategic measures aimed at ensuring such use of Information.
In addition, the Teijin Group establishes, revises, and abolishes standards as necessary to support the implementation of the Regulations. In particular, while recognizing that generative AI can contribute to improving operational efficiency and creating new value, we also recognize the need for appropriate management from the perspectives of legal compliance, information security, and the protection of third-party rights. Accordingly, we have established the Generative AI Usage Guidelines to promote the appropriate and responsible use of AI.
Generative AI Usage Guidelines
Main Content
【Principles for Using Generative AI】
- Approval must be obtained from the Information System Division of each company
- Do not enter confidential information and personal information (entry is limited to those within the scope approved)
- Do not easily trust the output of AI, and use it at your own risk after verifying and correcting it
【Prohibited Uses of Generative AI】
- Using generated products (materials, documents, computer programs, etc.) internally or externally without verifying them
- Creation of materials, papers, etc. for the purpose of evaluating the abilities and ideas of individuals or teams (excluding cases in which generative AI is used supplementarily)
- Using generative AI for something for which the use of generative AI is prohibited
- Creation of inventions, copyrighted works, or other intellectual property for the purpose of acquiring rights (excluding cases in which generative AI is used supplementarily)
- Use that results in the disclosure of the Teijin Group's trade secrets, internal-use-only information, confidential information of others, etc.
- Operations involving the handling of personal information
【Matters to be Noted When Entering Data】
- Data for which a third party holds the copyright
- Registered trademarks and registered designs
- Photographs or names of famous persons
- Personal information
- Confidential information disclosed by another party under an obligation of confidentiality
- The Teijin Group's trade secrets and internal-use-only information
【Matters to be Noted When Using Generated Products】
- Generated products may contain falsehoods
- The act of using generated products may infringe on someone's existing rights (Copyright infringement, Trademark/design infringement and False personal information/defamation)
- Intellectual property rights, such as copyrights, of generated products may not arise
- There is a possibility that generated products cannot be used for commercial purposes
- Be aware of the restrictions in the policies of generative AI
Information Security Management Structure
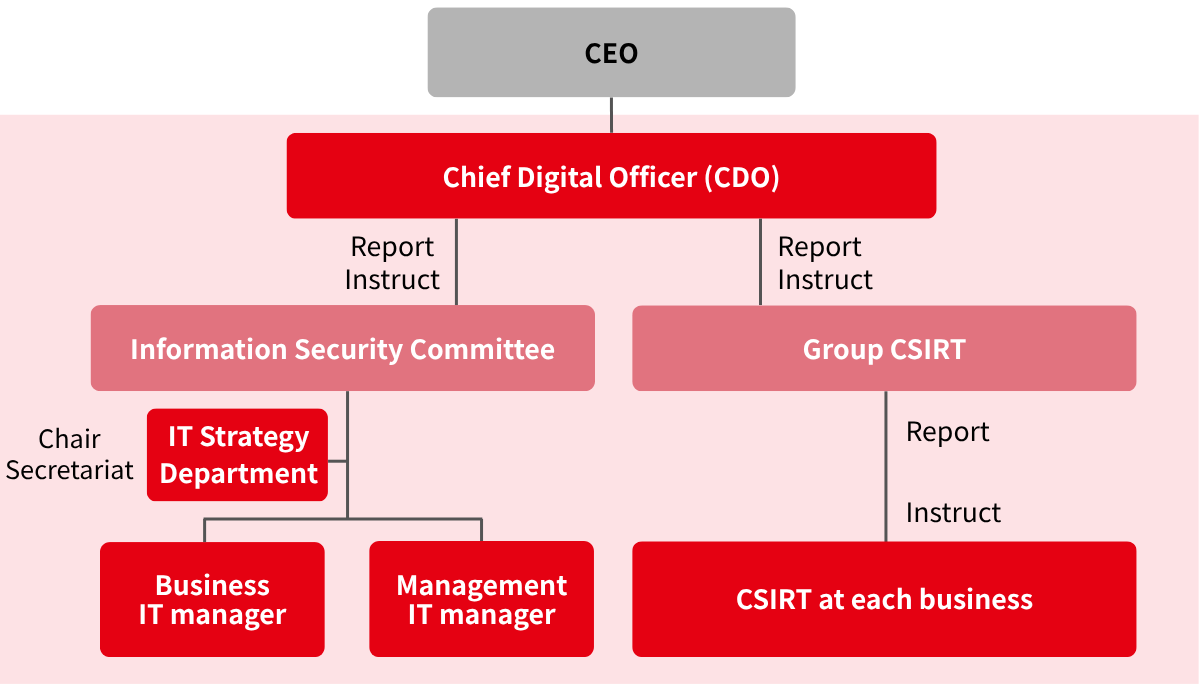
The Teijin Group has appointed a Chief Digital Officer (CDO) as the person responsible for overseeing global DX/IT governance, including IT policy, IT investment/costs, IT organization/human resources, information security, and AI implementation. The CDO acts as the Risk Management Owner for information security, and the Teijin Group has established an information management structure within the Group by clearly defining the roles and responsibilities of the general manager of the IT Strategy Department at Teijin, the IT managers of each business unit, department, and Group company, and all employees. Additionally, under the CDO's supervision, we have established the Information Security Committee, with the general manager of the IT Strategy Department serving as chairperson and the IT managers of each business unit and management organization participating as members. This committee considers and implements cross-group information security measures and educational activities. To respond to information security incidents, the Teijin Group has established a Group Computer Security Incident Response Team (CSIRT), which monitors our information systems and data for attacks and suspicious activity around the clock, while also continuously working to improve its response processes, including prevention, detection, response, and recurrence prevention. We have also been a member of the Nippon CSIRT Association (NCA) since 2016, through which we are able to utilize the latest threat intelligence and case studies from other companies in day-to-day security measures.
Group Information Security Management Structure
Measures for Information Security Management
The Teijin Group periodically reviews the management of information assets held and managed by each organization, such as information systems, networks, facilities, personal information, and confidential information. We strive to maintain and strengthen our level of information security by classifying these assets by importance, identifying threats, assessing risks, and then implementing appropriate countermeasures. To prepare for ransomware attacks and other threats, we implement technical measures including endpoint detection and response (EDR), data encryption, immutable backups, enhanced multi-factor authentication, and security log monitoring to ensure the integrity and confidentiality of data. We have also established reporting and response procedures for when security incidents occur, and maintain a 24/7 reporting system for suspicious emails and information security incidents, enabling their early detection and prompt response. In addition, we provide all executives and employees with regular e-learning programs and hands-on training to strengthen their practical response capabilities and raise information security awareness. In addition to these initiatives, the Corporate Auditing Department conducts information security audits for all Group companies from an independent standpoint, verifying the effectiveness of information security management and promoting its continuous improvement. As a result of these comprehensive efforts, no information security incidents with a significant impact on our business operations were identified in FY2025.
Escalation Process for Information Security Incidents
The Group Risk Management Regulations of the Teijin Group stipulate the reporting and handling procedures for incidents and accidents. We also have a system in place to receive reports from those who discover suspicious emails or security incidents 24 hours a day, 365 days a year.
Information Security Education
With the goal of enabling every employee to properly utilize information assets while responding to growing security risks, the Teijin Group works to ensure that each individual acquires the essential awareness and knowledge needed to protect the Group's information assets. To this end, we regularly provide information security education through e-learning and group work by organizational unit, along with hands-on response training using simulated targeted-attack emails for all executive officers and employees.
Appropriate Response to Personal Information Protection
We work to ensure compliance with laws and regulations in each country and region, and to thoroughly implement related measures through a system that assigns a "person responsible for protection of personal information".